Cybersecurity • 22 hours ago • Neha Jamwal
Introduction
For years, vulnerability management followed a relatively straightforward formula: discover vulnerabilities, assess their severity, patch affected systems and move on to the next batch. That model worked reasonably well when organizations had fewer applications, fewer connected devices and more predictable infrastructure. Today, however, enterprise environments are changing faster than traditional patching processes can keep up.
The sheer volume of vulnerabilities is becoming an operational challenge in its own right. Microsoft’s September 2026 Patch Tuesday addressed 972 vulnerabilities, including more than 100 classified as critical, illustrating the scale of the problem facing security and IT teams. At the same time, attackers are not waiting for organizations to work methodically through a vulnerability queue. They are looking for weaknesses that provide useful access to valuable systems, particularly vulnerabilities that are exposed, exploitable and already being used in real-world attacks.
That creates an uncomfortable reality for security leaders: an organization can be patching aggressively and still be exposed to significant risk.
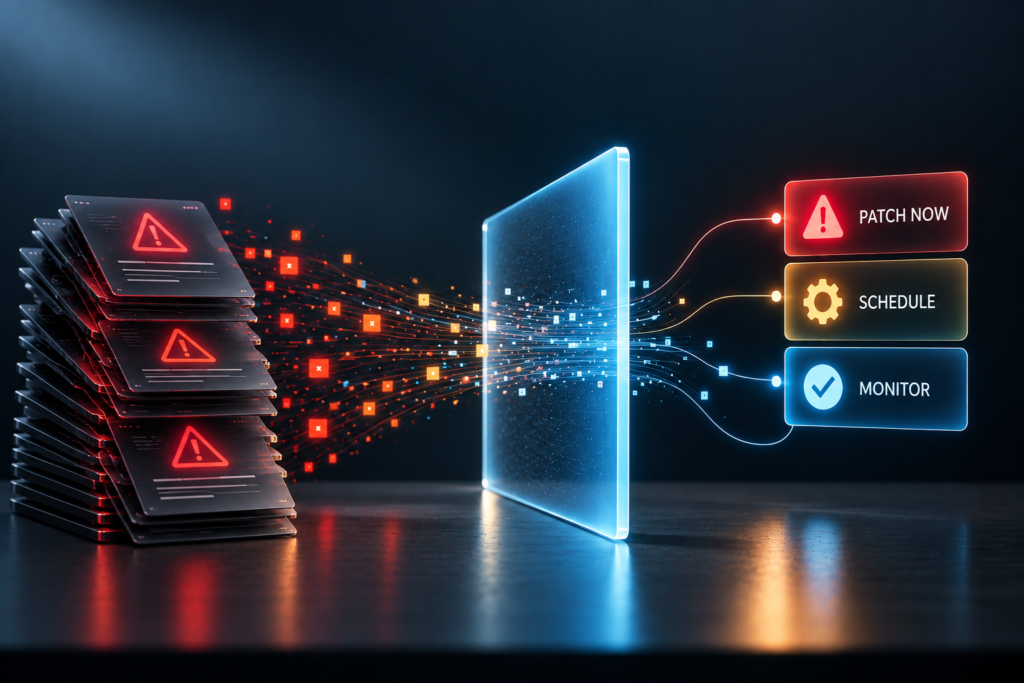
The answer is not to patch less. It is to become much more deliberate about what gets patched first, why it matters and how quickly the organization needs to respond.
Key Takeaways
- The growing volume of vulnerabilities makes blanket patching increasingly difficult to sustain.
- A vulnerability’s severity score does not necessarily represent the risk it poses to a specific organization.
- Vulnerabilities that are actively exploited deserve substantially greater attention than theoretical weaknesses.
- Patching can itself introduce operational risk when changes affect critical production environments.
- Vulnerability management is increasingly becoming an exposure-management problem.
- Automation and machine-readable vulnerability intelligence can help security teams prioritize remediation more effectively.
The Vulnerability Backlog Is Becoming a Security Problem of Its Own
The modern enterprise does not have a small, static set of systems waiting to be patched. It has cloud workloads, SaaS applications, endpoints, containers, APIs, network infrastructure, third-party software, operational technology and increasingly complex application dependencies. Each component can introduce vulnerabilities, and those vulnerabilities can change faster than traditional remediation cycles.
The result is a growing gap between what organizations know is vulnerable and what they can realistically remediate immediately.
This creates a difficult prioritization problem. If security teams treat every newly disclosed vulnerability as equally urgent, they risk overwhelming IT operations and consuming resources on weaknesses that may have little practical relevance to the organization’s attack surface. If they prioritize only by severity score, they may miss vulnerabilities that attackers are actively exploiting because those weaknesses happen to carry a lower theoretical rating.
The challenge, therefore, is no longer simply discovering vulnerabilities. It is determining which vulnerabilities create meaningful exposure right now.
That distinction becomes increasingly important as vulnerability volumes continue to grow. A backlog is not necessarily evidence of poor security performance. A poorly prioritized backlog, however, can become one.
CVSS Tells You Something. It Does Not Tell You Everything.
One of the most widely used tools for assessing vulnerability severity is the Common Vulnerability Scoring System (CVSS). CVSS provides a standardized score, typically ranging from 0 to 10, based on characteristics such as exploitability, required privileges, user interaction and potential impact.
CVSS is useful because it gives security teams a common language for discussing vulnerability severity. A critical score can quickly signal that a vulnerability deserves attention, particularly when security teams are dealing with thousands of vulnerabilities across a large environment.
But severity and organizational risk are not the same thing.
Consider two vulnerabilities. One might have a CVSS score of 9.8 but exist only on an isolated internal system with limited access and no known exploitation. Another might have a lower score but affect an internet-facing application that handles sensitive customer information and has already been targeted by attackers.
The second vulnerability could represent a much more immediate problem for that organization.
This is why modern vulnerability prioritization increasingly considers additional context, including whether a vulnerable asset is exposed to the internet, whether the asset is business-critical, whether exploitation has been observed and whether the vulnerability provides an attacker with a useful path toward other systems.
CVSS remains valuable. The mistake is treating it as the entire decision-making process.
Attackers Do Not Work From the CVE List
Security teams often think about vulnerabilities as entries in a database. Attackers think about them as opportunities.
A vulnerability becomes particularly dangerous when it can be connected to a realistic attack path. An internet-facing application may provide initial access. A compromised identity may then allow lateral movement. A vulnerable internal system could provide privilege escalation. From there, an attacker may reach sensitive data or critical infrastructure.
This means that the question security teams need to ask is not simply, “How severe is this vulnerability?”
It is also: “What could an attacker do with this vulnerability in our environment?”
The Known Exploited Vulnerabilities catalog maintained by the U.S. Cybersecurity and Infrastructure Security Agency is an important example of this shift. Rather than treating every disclosed vulnerability as equally urgent, it highlights vulnerabilities for which there is evidence of exploitation in the wild. Known exploitation does not automatically mean that every organization faces the same level of risk. Context still matters. But it provides an important signal that a vulnerability is not merely theoretical. The distinction between possible exploitation and observed exploitation is increasingly central to effective vulnerability management.
The Patch Itself Can Create Operational Risk
There is another problem with treating patching as an automatic security activity: patches can change production environments.
Security teams understandably want vulnerabilities fixed as quickly as possible. Operations teams, meanwhile, have to consider whether a patch could affect applications, integrations, infrastructure or business continuity.
That tension is not hypothetical. In September 2026, Microsoft released an emergency out-of-band Windows update after issues associated with the September security updates affected certain Hyper-V and Remote Desktop scenarios, among other reported problems.
The lesson is not that organizations should delay security updates. Rather, it demonstrates why patching has to be managed as an operational change as well as a security action.
A mature remediation process therefore needs to consider questions such as:
- What systems are affected?
- How critical are those systems to the business?
- Is the vulnerability actively exploited?
- Is there a workaround or compensating control?
- Can the patch be tested before broad deployment?
- What is the rollback plan if something goes wrong?
The goal is not to create bureaucracy around patching. It is to avoid replacing one form of risk with another.
The Attack Surface Is Too Dynamic for Periodic Patching Alone
Traditional patch cycles assume that the environment can be assessed, changes can be scheduled and vulnerabilities can be systematically remediated. That becomes harder when infrastructure itself is constantly changing.
Cloud workloads can appear and disappear within minutes. Containers can be replaced automatically. New software dependencies can enter an application through development pipelines. Employees can connect unmanaged devices. SaaS integrations can introduce new data flows without traditional infrastructure teams being directly involved.
A vulnerability assessment conducted today may therefore describe an environment that has already changed by tomorrow.
This is one reason vulnerability management is increasingly moving toward continuous exposure assessment. Instead of asking only which vulnerabilities exist, organizations are beginning to ask where those vulnerabilities sit within the broader environment and whether they create a realistic route to something valuable.
That requires bringing together vulnerability intelligence with asset inventories, identity information, network exposure, business context and attack-path analysis.
The result is a more useful question:
Where can an attacker actually get leverage?
Automation Needs to Move From Detection to Decision Support
Security organizations have invested heavily in tools that automatically discover vulnerabilities. The next challenge is making those systems better at helping organizations decide what to do about them.
Machine-readable security information is an important part of that transition. In September 2026, Microsoft announced that it was expanding its use of machine-readable Vulnerability Exploitability eXchange, or VEX, statements for Microsoft-assigned vulnerabilities. The goal is to provide more consistent information that can help organizations automate vulnerability analysis and reduce manual investigation.
This matters because security teams cannot manually investigate every vulnerability with the same level of detail.
Automation can help correlate multiple signals and surface vulnerabilities that deserve immediate attention. Instead of simply generating another alert, a modern vulnerability platform should increasingly be able to answer questions such as:
- Is the vulnerable system exposed?
- Is the affected asset business-critical?
- Is the vulnerability known to be exploited?
- Is there a viable attack path from the vulnerable asset to sensitive resources?
- Are compensating controls already reducing the risk?
- Is a patch available and operationally safe to deploy?
- What should happen if remediation cannot occur immediately?
The objective is not to eliminate human judgment. It is to ensure that human judgment is applied where it adds the most value.
From Vulnerability Management to Exposure Management
This is where the broader shift toward exposure management becomes important.
Vulnerability management focuses heavily on weaknesses. Exposure management takes a wider view of how weaknesses, assets, identities, configurations and attack paths combine to create opportunities for attackers.
That difference may sound subtle, but it changes the way organizations allocate security resources.
Imagine an enterprise with 10,000 known vulnerabilities. A traditional process might organize those vulnerabilities by severity and assign remediation deadlines. An exposure-oriented approach would attempt to identify the smaller subset that can realistically contribute to an attack against critical business assets.
That could include a medium-severity vulnerability on an internet-facing system with privileged access, while deprioritizing a higher-severity vulnerability on an isolated asset with strong compensating controls.
This does not mean ignoring lower-priority vulnerabilities. Organizations still need baseline patching, configuration management and lifecycle processes. The difference is that remediation becomes risk-driven rather than volume-driven.
The goal is no longer simply to reduce the number of vulnerabilities in a dashboard.
It is to reduce the number of meaningful opportunities available to an attacker.
What Enterprises Should Change
The shift away from blanket patching does not require organizations to abandon established patch-management programs. Instead, security leaders can strengthen them by adding greater context to remediation decisions.
A more mature approach can include:
- Exploit intelligence: Give greater urgency to vulnerabilities with credible evidence of active exploitation.
- Asset criticality: Connect vulnerabilities to the business importance of affected systems.
- Exposure: Identify internet-facing, externally accessible and otherwise reachable assets.
- Attack paths: Understand whether a vulnerability can help an attacker move toward privileged or sensitive resources.
- Compensating controls: Account for segmentation, endpoint protection, access restrictions and other controls that may reduce practical exposure.
- Operational impact: Evaluate whether remediation could disrupt critical services.
- Automation: Use machine-readable intelligence and automated correlation to reduce manual triage.
- Continuous assessment: Re-evaluate exposure as infrastructure and applications change rather than relying exclusively on periodic snapshots.
This approach also gives security teams a better way to communicate with business leaders. Instead of reporting that thousands of vulnerabilities remain open, they can explain which exposures represent the most meaningful business risk, what actions are being taken and where temporary controls are being used.
That is a much more useful conversation than simply debating whether the vulnerability backlog is getting smaller.
The Future of Patching Is Not Less Patching
The idea that enterprises should stop trying to patch everything can easily be misunderstood. The future is not about accepting vulnerable systems as inevitable or allowing security teams to ignore large portions of their infrastructure.
Patching remains one of the most important controls in cybersecurity.
What is changing is the expectation that patching alone can serve as a complete vulnerability-management strategy.
As environments become more distributed and vulnerability volumes continue to rise, organizations need to distinguish between vulnerabilities that are merely present and vulnerabilities that create meaningful exposure. They need to understand which assets matter, how attackers could reach them and which weaknesses can actually be used to create business impact.
That requires combining vulnerability intelligence with real-world context.
The organizations that adapt will still patch aggressively. The difference is that they will spend their fastest response cycles on the vulnerabilities that matter most, while using automation, compensating controls and structured remediation processes to manage everything else.
Conclusion
The central challenge in modern vulnerability management is no longer discovering vulnerabilities. Security tools are already very good at finding them.
The harder problem is deciding which ones deserve immediate action.
A constantly growing vulnerability backlog makes blanket prioritization increasingly impractical. CVSS provides an important measure of technical severity, but it cannot capture every factor that determines real-world organizational risk. Active exploitation, asset exposure, business criticality, attack paths and operational considerations all need to influence remediation decisions.
That is why the future of patching is likely to be less about chasing a perfect vulnerability scorecard and more about understanding enterprise exposure.
The question security leaders should ultimately be asking is not, “How many vulnerabilities have we patched?”
It is:
“Have we reduced the exposures that give attackers the most valuable paths into our organization?”
That is a much harder question to answer — but it is also a much more meaningful measure of security progress.